Auditor-Led GRC
Krypton GRC helps teams assess controls, understand compliance gaps, manage risks and organize audit evidence in one place. Built around an auditor-led approach, it helps you see what needs attention and decide what to do next.
Free Express Scan, no account needed · One assessment read against 27 frameworks · Led by a certified IT auditor
Or start inside the console: Try the Policy Tester · Preview an audit report. The report builds from your own work in the session: it starts empty and fills as you test.
Built by a CISA. Run like a PMP project.
Governed like your business depends on it.
Enter a website address to begin the checks supported by Krypton's Express Scan.
Enter a website address to run the scan.
✓ No installation required.
Knowing whether the right policies, controls and safeguards are in place can be difficult. Krypton helps you assess where you stand, identify gaps and plan practical next steps.
One scan. Mapped to 27 frameworks.
3 gaps found.
Checked the way I'd check it in an audit: Terry Afram-Kumi · CISA · PMP · Founder, Terafram
A sample. Yours takes under a minute. Paste your website in the scan box above.
To make compliance practical for every organization. One auditable scan that maps your internal controls across multiple frameworks, so you know your compliance gaps.
A world where compliance helps a business move instead of holding it back. Where any team can adopt new technology, including AI, with confidence, on an auditable pathway that proves responsible governance.
Three disciplines, one platform. CISA audit methodology means every finding is backed by evidence. PMP project discipline means every engagement runs in clear phases with visible progress. And AI security operations aligned to industry frameworks means you are covered on privacy, breach response, and AI governance, not just traditional compliance.
Your exam is on the calendar and the evidence lives in five different places. Start with the scan your auditor would run.
A customer's deal is waiting on your answers about SOC 2, access control and the AI your team uses. Get the gaps named first.
Your team is already pasting real work into AI tools. Find the governance gaps before they turn into incidents.
One effort, every framework. Answer once, map everywhere.
We probe your public footprint, encryption, headers, DNS, and walk you through a short questionnaire for the controls no scanner can see. Twenty minutes, not twenty meetings.
Every answer is scored once and mapped across 27 frameworks at the same time. Fix one control, watch your ISO, NIST and SOC 2 scores move together.
You get a gap report ranked by risk, not a 200-page PDF you'll never read. Fix it with your team, or bring me in and we'll close the worst gaps first, in phases, like a project should be run.
"Compliance is not a checklist. It's the proof that your business can be trusted. With data, with AI, with everything."
Terry Afram-Kumi, Founder, Terafram · CISA · PMP · MSc
Start Where You Stand
“I want to see my gaps.”
Run the free Express Scan on your own website. No account. The grade lands in under a minute.
Run the free Express Scan →“I want to test my own judgement.”
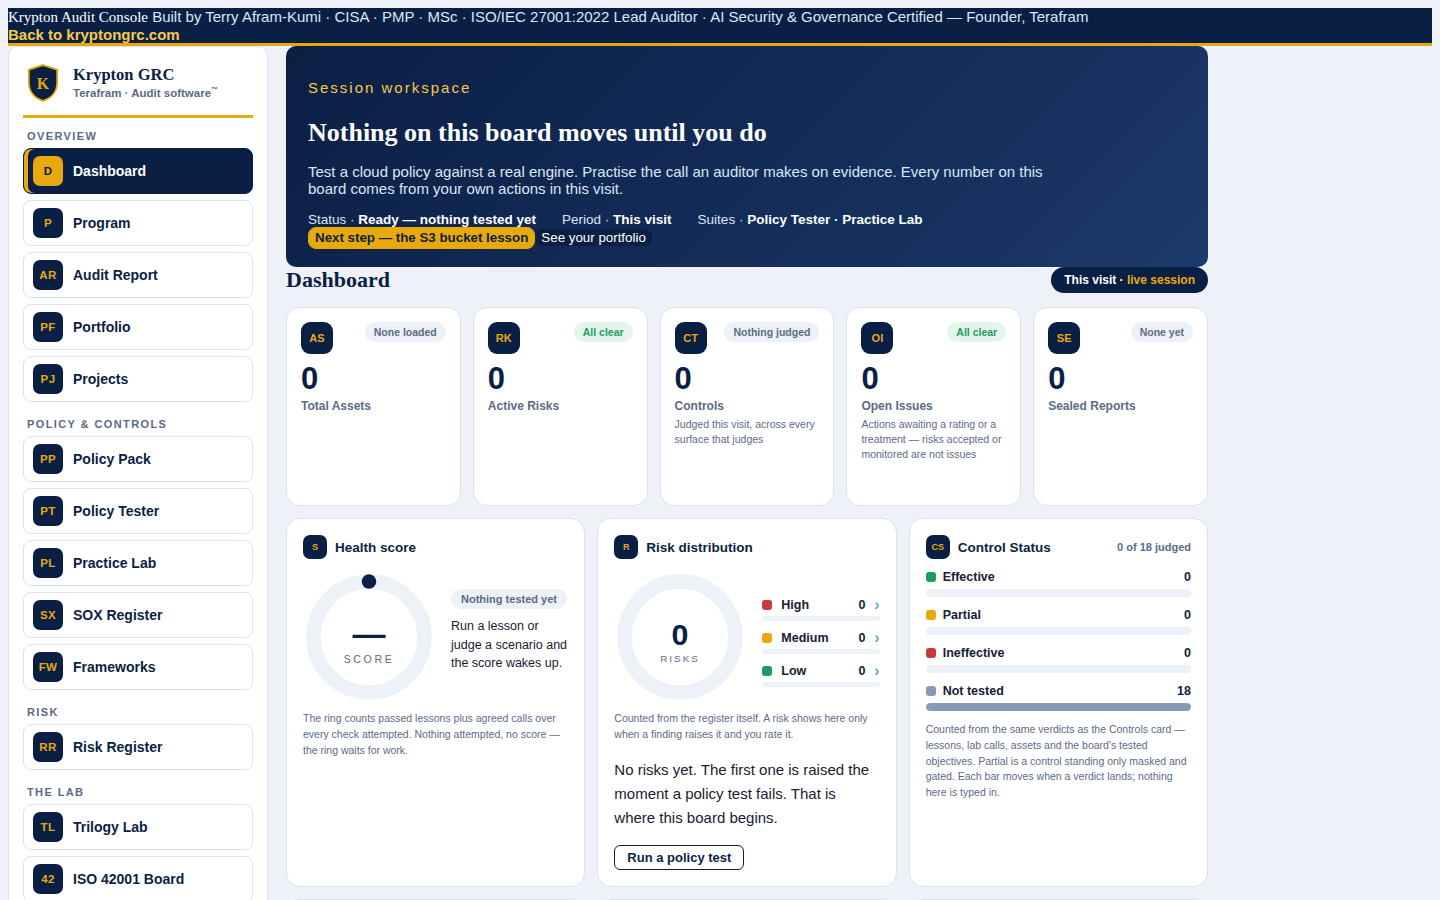
Open the Audit Console. Test policies, judge scenarios and watch the auditor's reasoning meet your call.
Open the Audit Console →“I want the auditor in the room.”
Book a free initial consultation. Thirty minutes with me. Your first move is named before we hang up.
Book a free initial consultation →Proactive Scanning
Your public footprint and controls, probed and scored in about twenty minutes.
Produces: a gap report across 27 frameworks, every finding carrying its evidence.
For: teams facing an audit, an exam or a customer security review.
Runtime AI Protection
Every AI prompt analyzed for injection, jailbreaks and PII exposure before it reaches your models.
Produces: a verdict on every prompt, blocked, cleaned or passed, logged as evidence.
For: teams whose people already put real work into AI tools.
Incident Response
When something happens, manage it in phases, with breach notification aligned to the laws that apply to you.
Produces: an incident worked in phases, with notification duties mapped to the people affected.
For: leaders who would rather rehearse the worst day before it arrives.
→ Know your gaps: one scan maps your controls across 27 frameworks at the same time with Krypton Scan, so you see what your auditor will see.
→ Stop AI threats at the door: every prompt is checked for injection, jailbreaks and PII exposure with Krypton Guard, before it reaches your models.
→ Respond in phases, not panic: incidents are worked step by step with Krypton Respond, with breach notification matched to the laws that apply to you.
→ Close the gaps with the auditor: work directly with Terry Afram-Kumi, CISA and PMP, to fix what the scan finds.
To learn more about how Krypton GRC can help your business, contact us or book a free initial consultation.
A policy on a shelf does not pass an audit. Evidence does. Krypton GRC ties every control to the evidence behind it, so you see exactly what your documentation supports.
One full scan, mapped to 27 frameworks.
| Control | Evidence | Status |
|---|---|---|
| Access Management | MFA policy + IdP export | ● |
| Change Management | Ticket history | ● |
| Incident Response | IR plan + tabletop record | ● |
| Data Protection | Encryption config | ● |
| Vendor Management | Vendor reviews | ● |
The Numbers, As They Stand Today
frameworks standing in a single assessment
controls in the book behind every scan
accounts needed for the free Express Scan. It runs cold, signed out
The Auditor Behind the Scan
I am Terry, founder of Terafram. As a CISA-certified auditor and PMP with an MSc, I watched businesses rush to adopt AI with no idea whether they were compliant, and no practical tool to find out. So I built Krypton GRC: the scan I wished existed, grounded in real audit methodology, priced for the businesses that need it most.
Book free initial consultationAI systems bring their own compliance surface. Krypton GRC covers that surface directly, and its AI governance assessment runs inside the same scan.
What the Engine Does
One assessment, checked by the engine against the 157 controls in its book and read across 27 frameworks. Every framework is measured against its own catalogue and every gap is named in the framework it belongs to.
One engine · one book · every framework read
Start free. Scale when your compliance scope does.
Free tier
Core community frameworks and open standards access.
Per evaluation & license
For rigorous compliance coverage across advanced frameworks.
Krypton GRC provides readiness and gap assessments, not certification. The scan shows where you stand; certification itself comes from accredited auditors.
The Full Consultancy Guide
Our complete guide to engagements run the Krypton way: CISA methodology, PMP discipline and AI security operations. The guide is shared with a consultation, not given away.
For: Teams weighing a full engagement with the auditor in the room.
Book a free initial consultation