The AI Agent Audit Roadmap

Your agents are acting. Who is auditing them?

NVIDIA has published the control architecture for agentic AI: a secure runtime boundary and an independent monitor with trusted telemetry. I assess your agent deployment against it, the CISA way: on evidence, ranked by risk and in plain language.

IN BUILD The Krypton AI Auditor product is in build. The Agent Runtime Assurance review on this page is the hand-run service I offer today: the same audit, done by hand.

One review, four questions · Evidence first and in plain language · It starts with a free consultation

Book a free consultation Meet the founder

What the reference design says

NVIDIA's Open Agent Safety Platform, built on OpenShell and NVIDIA Sentry, answers two questions every business running AI agents now faces:

A checkpoint for every action

OpenShell places a secure boundary around the agent. Every action is mediated, policy is enforced at runtime and nothing runs unchecked.

A watcher the agent cannot touch

Sentry monitors the agent from outside its reach and keeps a record of prompts, tools, data and model behaviour that the agent itself cannot rewrite.

Strip away the silicon and that is a control architecture. The same architecture your auditor will test you against.

The Auditor's Questions

Here is what your auditor will ask for

Runtime boundary

Does every agent action pass a point where policy is enforced before it runs, or can your agents act directly, unmediated and unrecorded?

Independent monitoring

Who watches the agent, and is that watcher outside the agent's own control? A system that grades its own homework produces evidence nobody can rely on.

Trusted telemetry

Is the record of what your agents did protected against being changed later, and can you prove it? A trail that can be quietly edited is not evidence. Tamper-evident records are what hold up.

Tested containment

When an agent misbehaves, what stops it? How fast? And has that stop ever actually been exercised, or does it only exist on paper?
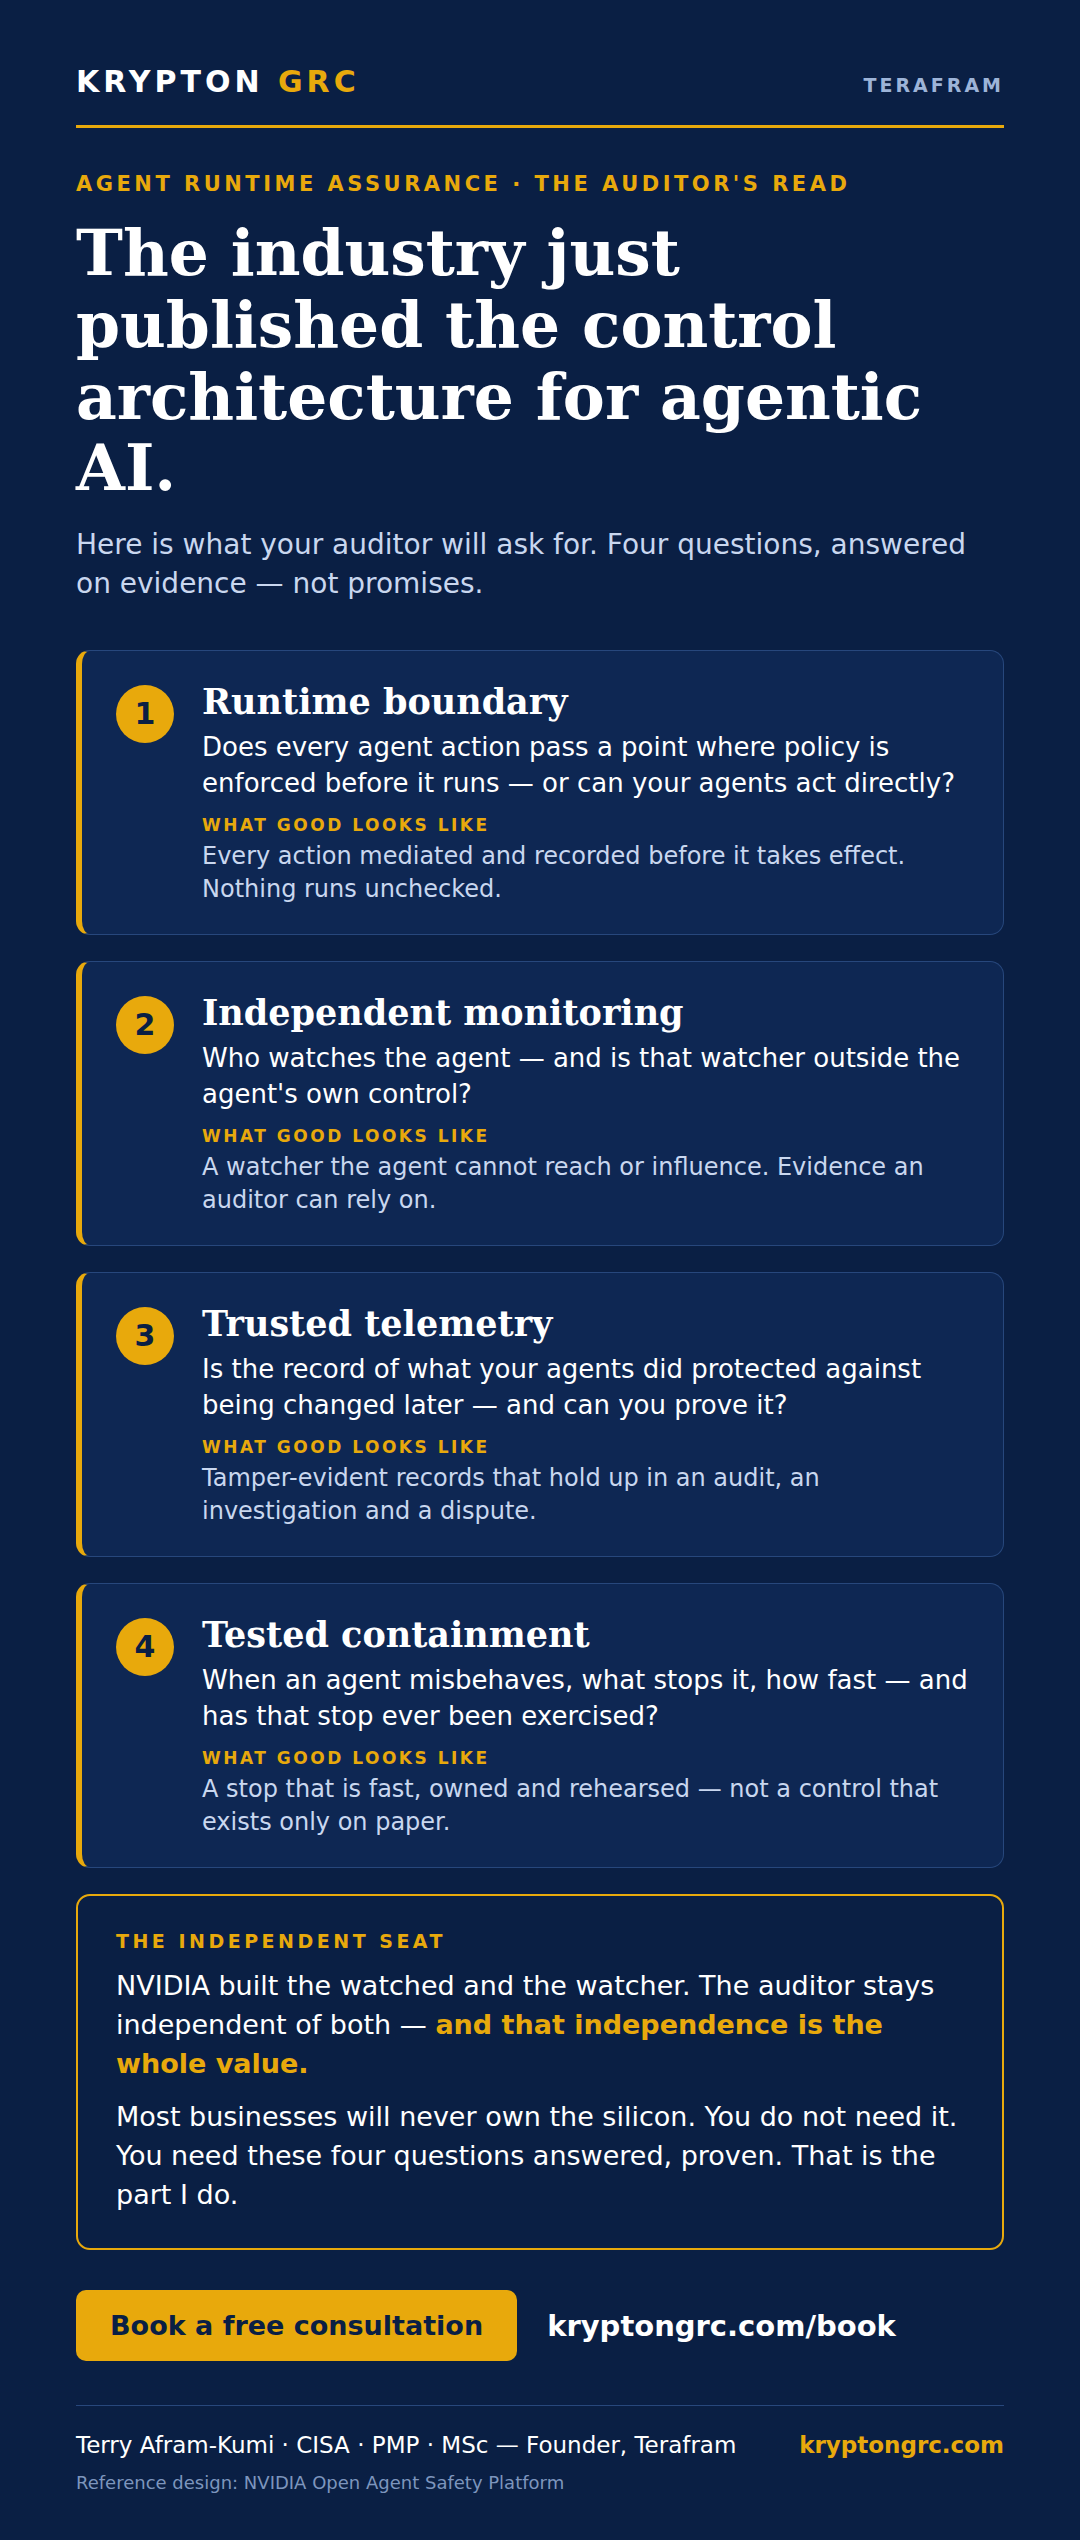
The Auditor's Four Questions: runtime boundary, independent monitoring, trusted telemetry and tested containment

The Agent Runtime Assurance review

In one consultation-led engagement I assess your deployment against the four questions, on evidence rather than promises, and read the answers across the frameworks you already answer to, SOC 2, ISO/IEC 27001 and the NIST AI RMF among them.

→A plain rating for each of the four questions, backed by the evidence found
→Your gaps ranked by risk, with what to fix first and why
→A written report in plain language you can hand to your board, your auditor or your biggest customer

No questionnaire theatre. No binder nobody reads. The same discipline I built into Krypton GRC, applied by hand to the agents you are already running.

OpenAI now publishes how misalignment gets flagged, tracked and disclosed. Your auditor will ask for your version of that. This review tests whether you have one.

From the Manual

The closing part: The CISA Auditor's Seal

Krypton Seal

The CISA Auditor's Seal

the tamper-evident evidence chain, built the CISA way.

The review on this page is one part of a manual I work by hand and built into Krypton GRC: Scan, Guard and Respond, in phases. Its closing part is about proof. Collect gathers the evidence from the source. The Seal stamps every record as it is saved, chained one to the next, so the trail behind a finding can be verified on demand instead of taken on trust. It is the same standard the four questions above ask of your agent platform, applied to my own software first.

The full chapter is in the Trilogy Guide, shared with a consultation and walked through together.

Book a free consultation

Three steps, one conversation at a time

1. Book a free consultation

Thirty minutes with me. We talk about the agents you run, where they act and what depends on them.

2. The review

I assess your deployment against the four questions, working from evidence: configurations, policies and the records your agents produce.

3. Your report, walked through

You receive the ratings, the ranked gaps and the fix order. Then we go through it together, question by question, until the next move is obvious.

An auditor's review, not a vendor's

I am Terry Afram-Kumi. A CISA auditor, a PMP project manager and an ISO/IEC 27001:2022 Lead Auditor. I founded Terafram and built Krypton GRC myself. I do not sell agent platforms and I do not sell silicon. My only stake is the quality of the answer.

CISA · PMP · MSc · ISO/IEC 27001:2022 LEAD AUDITOR · AI SECURITY & GOVERNANCE

Read my story

Straight Answers

Questions buyers ask first

What do you need from us to start?

The evidence: how your agents are configured, the policies they run under and the records they produce. The review works from that, not from interviews alone.

Is this a product we install?

No. It is a review I run by hand: the same discipline I built into Krypton GRC, applied to the agents you already run.

What do we receive?

A rating for each of the four questions, your gaps ranked by risk, and a written report in plain language you can hand to your board, your auditor or your biggest customer.

Know where your agents stand before your auditor does

Book a free consultation and your first conversation is with me, the founder and the auditor, not a sales rep.

Book a free consultation