Auditor-Led GRC

Better audits. Clearer risks. Stronger evidence.

Krypton GRC helps teams assess controls, understand compliance gaps, manage risks and organize audit evidence in one place.

Free Express Scan, no account needed · One assessment read against 104 frameworks · Led by a certified IT auditor

Check your website

The free Express Scan runs on the address you enter. No installation required.

Your compliance snapshot

Sample
80
Grade B

One scan. Mapped to 104 frameworks.
3 gaps found.

NIST CSF 2.0
90
ISO/IEC 27001
86
SOC 2
82
AI governance
62
✓ Real checks on your live site, not a paper form
✓ Every gap traced to a control. The CISA way
✓ Fix it, rescan, prove it

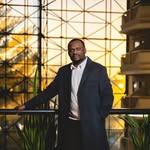
Checked the way I'd check it in an audit: Terry Afram-Kumi · CISA · PMP · Founder, Terafram

A sample. Yours takes under a minute. Paste your website in the scan box.

The Express Scan, live in this film: a real site, graded.
Built by a CISA. Run like a PMP project.

KryptonGRC Audit Approach

Three disciplines, one platform. CISA audit methodology means every finding is backed by evidence. PMP project discipline means every engagement runs in clear phases with visible progress. And AI security operations aligned to industry frameworks means you are covered on privacy, breach response, and AI governance, not just traditional compliance.

How it works

One effort, every framework. Answer once, map everywhere.

1

Scan

We probe your public footprint, encryption, headers, DNS, and walk you through a short questionnaire for the controls no scanner can see. Twenty minutes, not twenty meetings.

2

Map

Every answer is scored once and mapped across 104 frameworks at the same time. Fix one control, watch your ISO, NIST and SOC 2 scores move together.

3

Consult

You get a gap report ranked by risk, not a 200-page PDF you'll never read. Fix it with your team, or bring me in and we'll close the worst gaps first, in phases, like a project should be run.

Proactive Scanning

Krypton Scan.

Your public footprint and controls, probed and scored in about twenty minutes.

Produces: a gap report across 104 frameworks, every finding carrying its evidence.

For: teams facing an audit, an exam or a customer security review.

C

Evidence Collection

Krypton Collect.

Your cloud estate, read straight from the cloud itself, so its standing is produced from evidence, not questionnaires.

Produces: a standing of your cloud estate, every check carrying the evidence behind it.

For: teams who would rather show their evidence than describe it.

G

Runtime AI Protection

Krypton Guard.

Every AI prompt analyzed for injection, jailbreaks and PII exposure before it reaches your models.

Produces: a verdict on every prompt, blocked, cleaned or passed, logged as evidence.

For: teams whose people already put real work into AI tools.

Incident Response

Krypton Respond.

When something happens, manage it in phases, with breach notification aligned to the laws that apply to you.

Produces: an incident worked in phases, with notification duties mapped to the people affected.

For: leaders who would rather rehearse the worst day before it arrives.
Ask KryptonGRC A medallion

Ask KryptonGRC.

All ten products

Proof beats paperwork.

A policy on a shelf does not pass an audit. Evidence does. Krypton GRC ties every control to the evidence behind it, so you see exactly what your documentation supports.

ControlEvidenceStatus
Access ManagementMFA policy + IdP export● In place
Change ManagementTicket history● Gap
Incident ResponseIR plan + tabletop record● In place
Data ProtectionEncryption config● Gap
Vendor ManagementVendor reviews● In place

The Numbers, As They Stand Today

104

frameworks standing in a single assessment

0

accounts needed for the free Express Scan. It runs cold, signed out

The Auditor Behind the Scan

Terry Afram-Kumi

"Compliance is not a checklist. It's the proof that your business can be trusted. With data, with AI, with everything."

Found your gaps. Now let's fix them.

I am Terry, founder of Terafram. As a CISA-certified auditor and PMP with an MSc, I watched businesses rush to adopt AI with no idea whether they were compliant, and no practical tool to find out. So I built Krypton GRC: the scan I wished existed, grounded in real audit methodology, priced for the businesses that need it most.

Book free initial consultation

AI governance, inside the same assessment

AI systems bring their own compliance surface. Krypton GRC covers that surface directly, and its AI governance assessment runs inside the same scan.

ISO/IEC 42001 NIST AI RMF OWASP LLM Top 10 MITRE ATLAS

What the Engine Does

Frameworks we cover

One assessment, checked by the engine against its book and read across 104 frameworks. Every framework is measured against its own catalogue and every gap is named in the framework it belongs to.

ISO/IEC 27001:202293 of 93 — the full catalogue
NIST CSF 2.022 of 22 — the full catalogue
SOC 2 (Trust Services Criteria)61 of 61 — the full catalogue
PCI DSS (Payment Card Industry Data Security Standard) v4.0250 of 250 — the full catalogue
HIPAA (Health Insurance Portability and Accountability Act) Security Rule21 of 21 — the full catalogue
GDPR (General Data Protection Regulation, EU 2016/679)41 of 41 — the full catalogue
CIS Controls v8153 of 153 — the full catalogue
HITRUST (Health Information Trust Alliance) CSF19 of 19 — the full catalogue
NIST SP 800-53 (Rev. 5)273 of 273 — the full catalogue
CSA Cloud Controls Matrix v4.1207 of 207 — the full catalogue
ISO/IEC 42001:202361 of 61 — the full catalogue
COBIT (Control Objectives for Information and Related Technologies) 201933 of 33 — the full catalogue
NIST SP 800-171 (Rev. 3)97 of 97 — the full catalogue
CMMC (Cybersecurity Maturity Model Certification) 2.0 (Level 2)127 of 127 — the full catalogue
FedRAMP (Federal Risk and Authorization Management Program)18 of 18 — the full catalogue
NIST AI RMF 1.072 of 72 — the full catalogue
SOC 1 (SSAE 18 / ISAE 3402)7 of 7 — the full catalogue
ISO 9001:201528 of 28 — the full catalogue
OWASP Top 10:202510 of 10 — the full catalogue
OWASP API Security Top 10:202310 of 10 — the full catalogue
OWASP LLM (large language model) Top 10:202610 of 10 — the full catalogue
OWASP CWE249 of 249 — the full catalogue
MITRE ATT&CK (Enterprise)227 of 227 — the full catalogue
MITRE ATLAS (AI Threat Matrix)129 of 129 — 127 covered, 2 accounted
FFIEC (IT Examination Handbooks; CAT as it stood at its 2025 sunset)48 of 54 — 6 gaps named
FERPA (34 CFR Part 99)18 of 20 — 2 gaps named
FINRA (FINRA Rules and the 2026 Annual Regulatory Oversight Report)69 of 69 — 50 covered, 19 accounted

One engine · one book · every framework read

Pricing

Start free. Scale when your compliance scope does.

Community / Free

Free

Free tier

Core community frameworks and open standards access.

  • Assessment workspace
  • NIST & OWASP frameworks
  • Basic CSV reports
Start an assessment

Enterprise & Paid

By engagement

Per evaluation & license

For rigorous compliance coverage across advanced frameworks.

  • ISO 42001, SOC 1/2, ISO 27001
  • PCI DSS v4.0 & HITRUST CSF
  • Itemized quote calculator
Book a free initial consultation

Krypton GRC provides readiness and gap assessments, not certification. The scan shows where you stand; certification itself comes from accredited auditors.